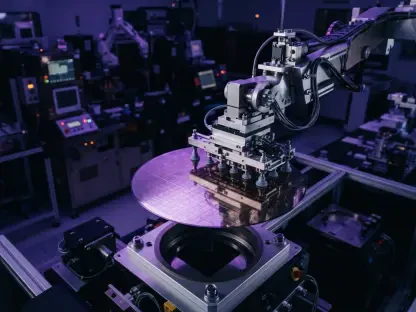
Attackers leverage hardware weaknesses through fault injection by manipulating voltage and clock speeds to trigger errors during critical authentication operations. This sophisticated method highlights a growing realization within the tech industry that cybersecurity is no longer just a software battleground. While engineers have spent decades perfecting firewalls and encryption algorithms, the physical integrity of the semiconductors and printed circuit boards that house this logic has often been overlooked as a secondary concern. Recent developments from 2026 to 2028 suggest that material imperfections, once considered mere manufacturing nuisances, are becoming primary attack vectors. When a microchip suffers from structural degradation or fabrication defects, its predictable behavior vanishes, leaving a window of opportunity for malicious actors to bypass security protocols. This shift in perspective necessitates viewing hardware quality as a foundational pillar of a robust security posture, where the silicon itself is scrutinized as closely as the code.
The Material Reality: How Manufacturing Flaws Undermine Logic
One of the most insidious physical defects currently plaguing high-density electronics is known as black pad syndrome. This condition occurs during the electroless nickel immersion gold plating process, where excessive phosphorus levels lead to the corrosion of the nickel layer. The resulting brittle intermetallic joint creates high-resistance connections that are prone to intermittent electrical failures. In a standard consumer device, this might cause a simple reboot, but in a security controller or a cryptographic module, these micro-interruptions can be catastrophic. When the physical connection between a processor and its secure memory is unstable, the timing of data transfers becomes inconsistent. Attackers can monitor these fluctuations to perform side-channel attacks, extracting sensitive keys by analyzing the power consumption patterns associated with these physical instabilities. Furthermore, the presence of such defects makes it much easier to induce the specific fault injections needed to bypass secure boot.
Beyond structural corrosion, the thermal management of silicon chips plays a vital role in maintaining the integrity of cryptographic operations. As chips age or suffer from minor manufacturing variances, their ability to dissipate heat evenly can diminish, creating localized hotspots that alter the transistor switching speeds. These variations allow for a technique where an attacker intentionally stresses a component through environmental manipulation to create a predictable error. By pushing a slightly defective component just beyond its operational threshold, an adversary can bypass digital signature verification or trick a device into entering a debug mode that should have been permanently disabled. This interplay between physical thermodynamics and digital logic proves that the silicon substrate is not a perfect, abstract platform but a physical medium with inherent limits. Ensuring long-term security requires recognizing that a chip’s physical health directly correlates with its ability to maintain a consistent logical state over time.
Hardware Provenance: Strategic Mitigations for Supply Chain Integrity
The global semiconductor supply chain is currently facing an unprecedented challenge from the proliferation of counterfeit and recycled components. According to industry watchdogs like ERAI, the complexity of these fake parts has evolved, with many now capable of passing basic electrical tests while hiding deep-seated reliability issues. These components are often harvested from electronic waste, then sanded down and relabeled to appear as high-grade, military-spec hardware. While they may function correctly upon initial installation, their previous operational history means they are much closer to the end of their lifecycle than a brand-new part. This hidden wear and tear introduces unpredictable variables into critical systems, such as healthcare monitoring devices. For a security professional, the danger lies in the fact that these recycled chips often lack consistent electrical characteristics, creating noisy signals that can be exploited by signal analysis tools to recover private encryption keys or other data.
To mitigate these physical risks, industry leaders prioritized a holistic security lifecycle that integrated hardware integrity directly into the procurement process. Organizations transitioned away from purchasing through unauthorized brokers and instead demanded rigorous manufacturing documentation and a verifiable chain of custody for every microchip. Advanced visual inspection techniques, such as X-ray microscopy, became standard procedures for identifying internal structural flaws before assembly. The implementation of system-level redundancies allowed for the detection of anomalous behavior at the hardware level, where secondary monitoring chips identified if a primary processor was behaving erratically. Future considerations shifted toward the adoption of physically unclonable functions that utilized inherent silicon variations for key generation. This proactive approach ensured that physical quality was treated with the same scrutiny as software code. By integrating these safeguards, organizations successfully closed the gap between logic and reality.