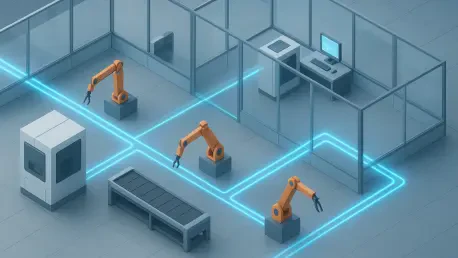
Threat actors are now utilizing artificial intelligence to clone executive voices and craft hyper-targeted social engineering attacks against industrial organizations. This shift represents a massive escalation in the complexity of threats facing the manufacturing world today. As the push for “smart factory” status continues, the lines between digital innovation and operational vulnerability have become dangerously blurred. Connectivity to cloud-native platforms and real-time data analytics offers immense productivity gains, yet it simultaneously erodes the physical and logical barriers that once isolated factory floors from global networks. Today, a manufacturer’s competitive advantage is no longer just a product of its assembly line efficiency, but also its ability to maintain uptime against an invisible, persistent adversary. Transitioning from isolated silos to interconnected ecosystems requires a complete reimagining of safety protocols, where digital security is now viewed with the same life-and-death gravity as physical plant safety.
Protecting Legacy Infrastructure and Supply Chains
Industrial Security: Protecting Fragile Control Systems
The foundational challenge within modern manufacturing plants lies in the persistence of legacy hardware that was never intended for an internet-connected world. Programmable logic controllers and human-machine interfaces often operate on outdated firmware that lacks the computational overhead required for modern encryption or robust authentication. These devices, many of which have been in service for decades and are expected to run through 2028, create a fragile environment where even basic security activities can be catastrophic. For instance, an active network scan designed to identify vulnerabilities can inadvertently overwhelm a sensitive controller, leading to an immediate production halt or physical damage to expensive machinery. This technical friction creates a situation where the very tools used to protect IT environments become threats themselves within the OT landscape. Consequently, security teams must treat these legacy components with extreme care to ensure the safety of the entire production line.
Third-Party Access: Managing Supply Chain Backdoors
Technical mitigations for vendor access must move away from convenience-based shared accounts toward a model of strict identity management. Replacing generic credentials with named accounts and implementing just-in-time access ensures that permissions are granted only for the duration of a specific task and revoked immediately afterward. Furthermore, organizations are transitioning from vulnerable SMS-based multi-factor authentication to phishing-resistant hardware keys, such as FIDO2-compliant devices, to secure these high-risk entry points. Network segmentation plays an equally vital role here by placing all third-party traffic into isolated zones where vendors can only interact with the specific assets they are contracted to maintain. By combining these technical controls with contractual requirements for strict breach-notification windows, manufacturers can build a more resilient relationship with their supply chain, ensuring that a single compromised link does not lead to a total systemic failure within the facility infrastructure.
Strengthening Resilience Through Identity and Intelligence
Identity Management: Moving Beyond Static Compliance
For too long, the manufacturing sector has relied on periodic compliance audits as a primary measure of security health. However, these audits represent only a single point in time and often fail to capture the dynamic nature of modern cyber threats. Attackers do not wait for the next audit cycle; they operate continuously, looking for ways to exploit stolen credentials rather than attempting to break through complex firewall configurations. This shift has made identity the new security perimeter, as the majority of modern breaches involve logging in with legitimate but compromised accounts. When a malicious actor hijacks a valid session, they can move through the network undetected, appearing to the system as a regular employee or authorized contractor. To combat this, manufacturers must transition toward a strategy of continuous monitoring that treats every account login as a potential risk factor, moving beyond the static checkbox mentality that compliance frameworks often encourage at the present time in the industry.
AI Defense: Defending Against Automated Threats
Manufacturers ultimately recognized that defending against artificial intelligence required a dual strategy focused on both external threats and internal vulnerabilities. While threat actors used AI to enhance social engineering, organizations responded by establishing dedicated detection frameworks that monitored automated interactions at the prompt level. This oversight ensured that the drive for automation did not come at the expense of operational integrity. To gain support for these initiatives, security leaders reframed cyber risk as a financial metric, quantifying the specific cost of potential downtime in terms of lost production and customer churn. This shift transformed cybersecurity into a strategic investment that preserved a manufacturer’s competitive edge. By integrating these defenses, companies successfully maintained a secure production line, proving that resilience was a core driver of excellence. These comprehensive steps ensured that the digital transformation of the factory floor remained a secure source of industrial value.